Product Security Architect · Automotive & embedded systems

Building security into products, from architecture to testing.

I’m Adel Belasker. I help engineering teams turn security risks and regulatory expectations into concrete architecture decisions, development practices, and test evidence — grounded in years of hands-on embedded and automotive engineering.

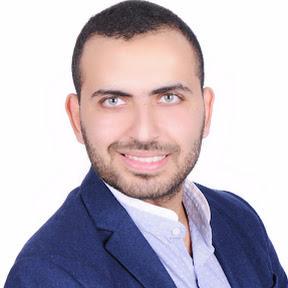
Portrait of Adel Belasker
Adel Belasker CISSP · Stuttgart region, Germany

Focus areas

Security that holds up across the product lifecycle.

Most security problems in products are decided early — in the architecture, the process, and what gets tested. That is where I focus.

01

Security architecture

Turning product context and threat analysis into security concepts, requirements, and architecture decisions that engineering teams can actually implement.

  • Threat analysis and risk assessment (TARA)
  • Security concepts and requirements
  • Architecture reviews for connected systems
02

Secure development process

Designing security activities, reviews, and work products that fit how product teams already develop and deliver — and that produce evidence worth having.

  • Process definition, piloting, and rollout
  • Security work products and reviews
  • Mapping standards to engineering activities
03

Security testing & validation

Shaping test strategy around the security assumptions that matter, from component interfaces to the full system — and automating it where it pays off.

  • Security test strategy
  • Penetration testing of embedded devices
  • Test automation for networked ECUs

Standards & regulation in practice

From requirement text to engineering work.

Regulation sets the expectation; engineering has to make it real. I focus on the practical connection between the two.

Automotive · UNECE

UN Regulation No. 155

Requires vehicle manufacturers to run a certified cyber security management system (CSMS) and to demonstrate cybersecurity for each vehicle type seeking approval.

Official source

Automotive · Engineering standard

ISO/SAE 21434

Defines cybersecurity engineering for road vehicles across the lifecycle — from concept and threat analysis through development, production, and operations.

Official source

Cross-sector · EU regulation

EU Cyber Resilience Act

Sets cybersecurity requirements for products with digital elements on the EU market, covering secure design, vulnerability handling, and support over the product’s lifetime.

Official source

Summaries are educational. How these requirements apply depends on the product, the organization, and its conformity context; they are not legal advice or a conformity assessment.
Experience

From embedded code to security architecture.

I started by writing and testing the software that runs inside devices. That hands-on foundation shapes how I approach security today: concrete, testable, and close to the engineering.

Full profile on LinkedIn
  1. 2022 — today

    Senior Cyber Security Architect & Process Owner

    Automotive industry

    Owns a secure vehicle development process from piloting to rollout, leads the vehicle security testing strategy, and drives cybersecurity activities during development of vehicles and components. Expert member of VDA AK11 for ISO/SAE 21434.

  2. 2019 — 2022

    Automotive Software Engineer

    Adaptive AUTOSAR

    Developed Adaptive AUTOSAR applications in C++, established TLS-secured communication between applications, and automated integration tests over SOME/IP, UDS, and DoIP.

  3. 2018 — 2019

    IoT Software Engineer

    Connected devices

    Built embedded C/C++ software across the full lifecycle, from specification and design through testing and release.

  4. 2018

    Master’s thesis in automotive security

    Industry research project

    Built an automated penetration testing tool for automotive devices over Ethernet — scheduling sequential and parallel attacks and evaluating the robustness of ECUs.

  5. 2015 — 2018

    Master of Engineering, Computer Science

    ENSI — École Nationale des Sciences de l’Informatique

Writing & training

Practical guidance, in progress.

I’m building a library of field guides for teams who need to turn product security into everyday engineering decisions. Focused training will follow. Topics I’m working on:

  • Planned

    From threat analysis to test cases

    Tracing threats and security requirements all the way to verification evidence.

  • Planned

    A secure development process teams will use

    Which activities and work products add value — and which only add paperwork.

  • Planned

    The Cyber Resilience Act for embedded teams

    What the regulation asks for, read from an engineering point of view.

Contact

Working through a product security challenge?

I’m happy to exchange ideas with practitioners, discuss collaboration, or talk through how security fits into your product development. LinkedIn is the best way to reach me.

Message me on LinkedIn